
IBACTP® — International Board of AI, Cybersecurity & Technology Professionals
Governance, Risk & Compliance Resources

Enterprise Risk Management

Quantifying Technology, Third-Party & Supply-Chain Risk

Technology risk is enterprise risk. Organizations must identify, evaluate, and prioritize digital exposures—including software dependencies, cloud providers, legacy debt, and cyber threats—using structured risk methodologies.

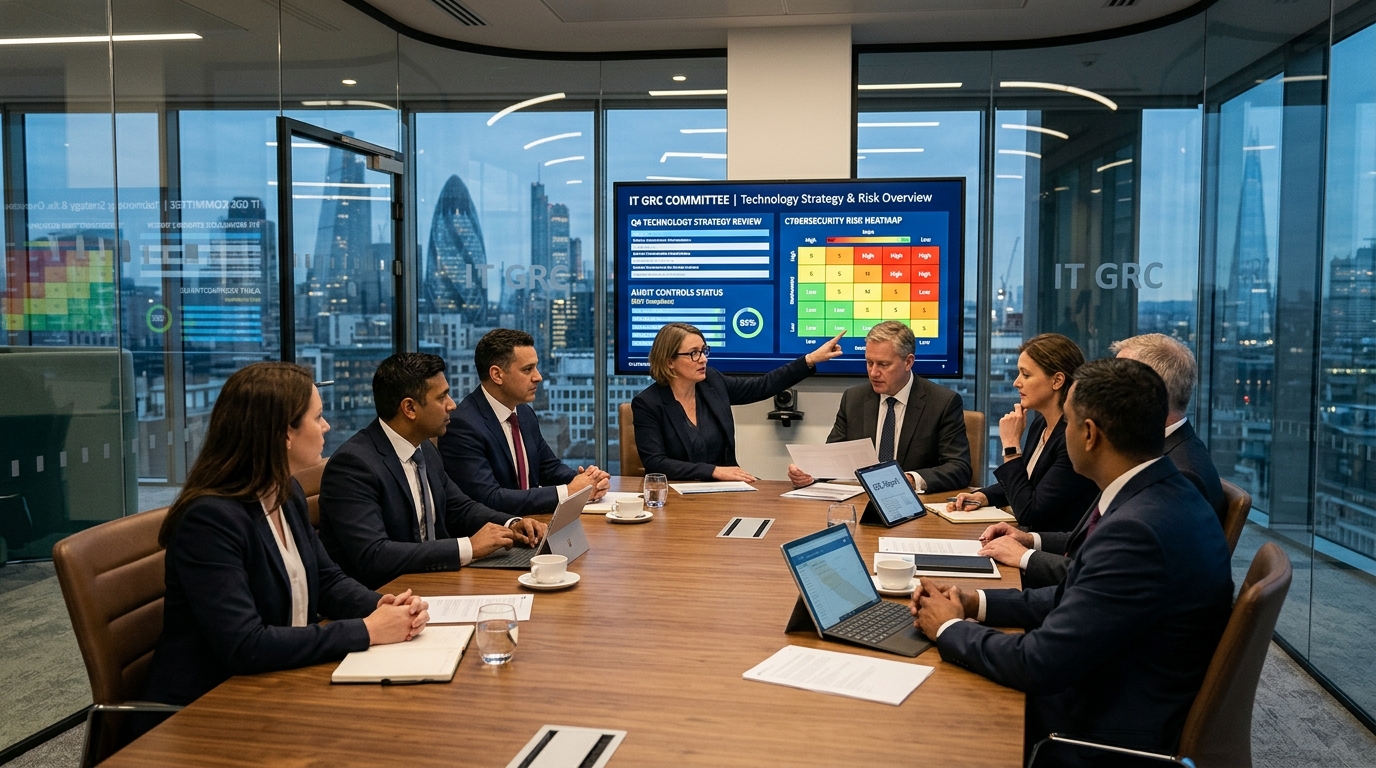
Technology governance and board risk review
AI governance and assurance laboratory
Risk and compliance working session
Governance, Risk & Compliance Enterprise Risk Management
Governance, Risk & Compliance resource centers

Select a center to explore guidance, standards and practitioner resources

Resource Library

Quantifying Technology, Third-Party & Supply-Chain Risk

Cybersecurity Soc Analysts
01

Quantifying Technology, Third-Party & Supply-Chain Risk

Technology risk is enterprise risk. Organizations must identify, evaluate, and prioritize digital exposures—including software dependencies, cloud providers, legacy debt, and cyber threats—using structured risk methodologies.

The IBACTP® Enterprise Risk Management Center provides risk analysts, compliance directors, and technology professionals with quantitative and qualitative frameworks for building transparent, actionable risk registers.
It Governance Grc Board Review
02

ENTERPRISE RISK ASSESSMENT METHODOLOGY

Risk Management Lifecycle

  • Identify
  • Assess
  • Treat
  • Monitor
  • Report

Core Risk Treatment Options

  • Mitigation: Implementing technical, administrative, or physical controls to reduce likelihood or impact below the risk threshold.
  • Transfer: Reallocating risk impact through contractual agreements, cyber insurance policies, or third-party warranties.
  • Avoidance: Discontinuing high-risk activities, decommissioning vulnerable legacy software, or terminating risky integrations.
  • Acceptance: Consciously acknowledging residual risk that falls within documented organizational risk tolerance limits.
Cloud Infrastructure Data Center
03

THIRD-PARTY & SUPPLY CHAIN RISK MANAGEMENT (TPCRM)

Over 60% of enterprise security incidents originate from third-party vendors, suppliers, or outsourced contractors. Effective supply chain risk management requires comprehensive lifecycle oversight:

Supply Chain Risk Management Pillars

  • Vendor Due Diligence: Pre-contract security assessments, SOC 2 Type II review, and ISO 27001 verification.
  • Contractual Security SLAs: Enforcing notification deadlines, mandatory MFA, encryption at rest/transit, and right-to-audit clauses.
  • Software Bill of Materials (SBOM): Tracking open-source dependencies and nested libraries to identify zero-day vulnerabilities quickly.
  • Continuous Vendor Monitoring: Real-time dark-web monitoring, credential breach intelligence, and vendor security ratings.
Governance, Risk & Compliance Resources

Turn Guidance Into Verified Competence

Pair these resources with an IBACTP® credential that validates the competence they describe.